What is an IP Stresser or IP Booter tool
Learn what a security testing console does, when teams use it legally, and how to run your first authorized check with clear scope and documentation.
Read: What is an IP Stresser or IP Booter tool

Tired of wasting money on weak IP Booter or Web-Stresser tools? ShutDown IPStresser is one of the most effective IP stresser and booter panels on the market.

ShutDown develops an advanced Layer4 & Layer7 resilience testing network for testing defensive controls. We provide world-class resilience simulation services to companies and enterprises.
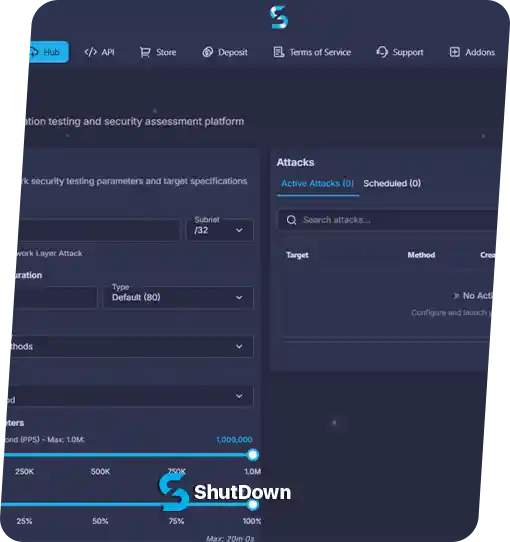
ShutDown is built for authorized security testing with a powerful IP stresser and IP booter: Layer 4 and Layer 7 resilience checks, firewall validation, and pentest-style load scenarios. Start with the free tier or scale to enterprise concurrency when your program needs deeper coverage. Every method is selectable from the dashboard with clear duration and protocol controls.

Searching for an IP stresser service?
If you Loaded up here, you just found the best IP booter to stress test any of your application Layer7, Layer4 ,UDP ,TCP,ICMP,HTTP2/HTTP1.

Best technology available on the market
High-bandwidth servers let you run authorized load and security testing with no delays, an instant stresser task queue, and full control over every run.

Interested to see what we have to offer?
Register today and you can try out our services for free!
ShutDown was created in early 2018 under a different name, offering a reliable, professional IP stresser and security testing service at an affordable price. Our business model is built around customers, and we work every day to keep services dependable.
Use ShutDown only on infrastructure you own or have explicit written authorization to test. We support letter-of-authorization workflows, encrypted operations, and clear acceptable-use rules so security teams can document resilience work for auditors, clients, and internal stakeholders.
Our large IP stresser capacity keeps your security runs stable and reliable. Subscribing means predictable performance when you validate infrastructure.
We offer one of the most capable, user-friendly IP stresser dashboards on the market built for fast setup, clear metrics, and repeatable stress testing.

Best booter & free security testing
try for free
Every capability below supports legitimate testing on systems you own or have written permission to test. Combine encrypted operations, rapid queueing, and bypass-aware methods to stress WAFs, CDNs, and custom rule sets without misleading claims or log sharing. Results stay in your control for internal reporting.
No logs kept, All data is encrypted, everything is coded with privacy protection in mind Your privacy is safe with us.
Read MoreOur advanced Support Team replies with in 24 hours at all regions, Your time has the highest value if you need any help contact us.
Read MoreLatest Bypass Methods we can bypass 95% of the firewall."CDN" "CDNFLY" "Cloudflare""Amazon" "Microsoft" "Hetzner" "Google" "Contabo" "NFO"And more!
Read MoreOur testing platform is custom-built by experienced engineersregistration and billing are automated, and we do not share logs with third parties.
Read MoreLatest technology and high-capacity networks power the platform. We guarantee* that your authorized security test traffic is delivered at least 99% of the requested rate,
Read MoreWe offer powerful IP stresser servers with high bandwidth to generate controlled security tests for your servers and sites. Runs start instantly, outcomes are predictable, and you configure duration in seconds or minutes.
Global capacity supports IPv4 and IPv6 stresser targets, mixed protocol profiles, and repeatable schedules for teams validating CDN edges, origin shields, and custom WAF rules before production traffic spikes.
Network
ShutDown
IPV4 & IPV6
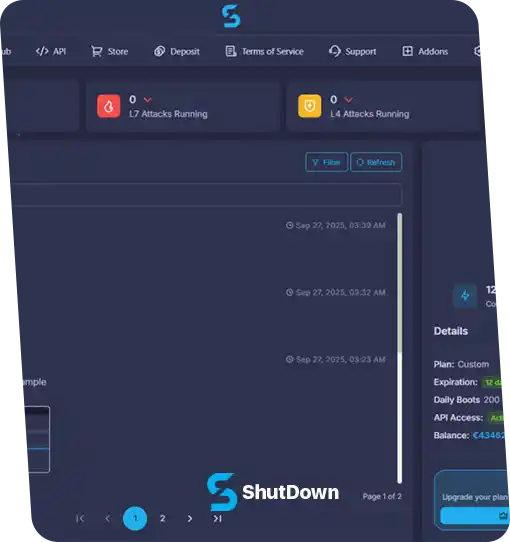
Our service is intended for companies and enterprises who want to test their servers or websites, or for system administrators. As a professional IP stresser and booter platform, ShutDown helps uncover weak zones, shows how properties stand up to high-load resilience scenarios, and supports authorized load testing of your own or customer-approved assets using diverse protocols.

For businesses or advanced users who need deeper stresser and security testing capacity, ShutDown offers premium packages with more resources and customization.

Unlock the testing hub with tunable settings. Exercise defenses against hardened targets, including those with custom WAF or filtering rules, through an interface built for operators.
These figures reflect live platform capacity and active customer programs—not placeholders. ShutDown invests in bandwidth, method diversity, and uptime so authorized tests run when you schedule them. Capacity scales with demand while keeping queue latency low for recurring pentest windows.
55+
Powerfull Methods400M RPS
Network Capacity900+ Gigs
L4 Network Capacity700+
Active Customers

Feedback from operators running authorized resilience programs—from free-tier evaluations to enterprise pentest schedules. Plan tiers reflect the package each customer used when sharing their experience. Reviews highlight uptime, support response, and realistic test delivery.

Compare tiers by concurrency, session limits, and advanced access. All plans include core Layer 4 and Layer 7 methods; paid packages add longer durations, higher daily limits, API access, and priority support for production security teams.
All subscriptions are billed securely with automatic activation once your payment is confirmed. Upgrade or downgrade between Destroyer and Eneterprice when your program needs more concurrent tests, longer durations, or API automation. The free tier remains available for evaluation—register, verify your targets, and scale only when your authorized testing scope grows. Enterprise teams can request custom concurrency, dedicated support channels, and recurring test windows aligned to change-management calendars.
Answers below cover billing, supported protocols, account sharing, and authorized targets. Contact support if you need help documenting ownership or setting up a letter of authorization before testing.
There are many websites that claim to be the best testing platform and promise unrealistic results. ShutDown takes pride in serving the community for over 10 years with honest, reliable solutions without misleading titles.
We do only accept cryptocurrencies in ShutDown,The Cryptocurrencies we curent support are: Bitcoin(BTC) | Ethereum(ETH) | Litecoin(LTC) | Monero(XMR) | USDT(TRC20) | USDT(ERC20). Our payment system is fully automatic ensuring every user gets the desired package at the first confirmation on the blockchain, usually within 5-10 minutes. For privacy and security we only accept crypto currency
We use spoofed IP's from range 1.0.0.0 - 255.255.255.255[Excluding private ips like: 127.0.0.1], ports 0 - 44405, IP Protocols UDP, TCP, ICMP, SYN,PSH,ACK,URG,FIN.
Based on our terms and conditions, you can not share your account, share your API or sell your account to anyone else. If the system detects such an account, it will auto-ban the account and you will lose access to your membership.
We do not allow testing government, bank, or educational properties without verified authorization. If you own one of those assets, contact support with proof of ownership and written permission to run an authorized security test. To protect your network, you can also blacklist your IP free: submit a free IP blacklist or free domain blacklist request via Contact (subject: Free Blacklist Request) or Telegram so your ranges stay excluded from stress tests. Violations may result in account closure without refund.
ShutDown provides a free IP blacklist and free domain blacklist so owners can protect IPs, CIDR ranges, and domains from unauthorized IP stresser or IP booter tests—at no cost. To blacklist an IP free (or request a free IP blocklist / free network blacklist), open Contact, select subject “Free Blacklist Request,” and submit the IPv4/IPv6 addresses, CIDRs, hostnames, or domains you want added to the free blacklist; include ownership proof when possible for faster approval. You can also request free blacklisting via Telegram support. Once approved, those targets stay blocked on our stress testing panel. See the Fair Use Policy for details.
Guides explain console basics, concurrency tuning, Layer 4 versus Layer 7 simulations, and enterprise compliance. Each article uses plain language with practical checkpoints for defenders and authorized testers. New posts cover platform updates and testing methodology.
Learn what a security testing console does, when teams use it legally, and how to run your first authorized check with clear scope and documentation.
Read: What is an IP Stresser or IP Booter tool
Step through planning, target verification, and interpreting results when running authorized website or server resilience tests with realistic traffic profiles.
Read: How to start a DDoS attack on a website
Understand resilience scenario types, protocol layers, and how different attack architectures map to defensive controls you can validate in staging.
Read: Network Attack Categories: From Volume based to DDoS
See which platform features matter most in 2026: bypass methods, capacity, uptime, privacy policies, and support for Layer 4 and Layer 7 workloads.
Read: Top Features That Make ShutDown the #1 IP Booter in 2026
Explore how authorized stress testing supports firewall tuning, SOC drills, and compliance evidence without crossing into unauthorized targeting.
Read: The Role of IP Stressers in Cybersecurity & Firewall Testing
Configure advanced concurrency, bypass options, and automation hooks for repeatable pentest-style runs across approved infrastructure.
Read: Step-by-Step Setup for Advanced IP Stresser Configurations
Choose safe concurrency levels that match your hardware, SLAs, and monitoring stack so tests reveal limits instead of causing avoidable outages.
Read: How to Choose the Right Concurrency Level for Stress Testing
Review enterprise deployment models—managed, self-service, and continuous validation—and when each fits regulated or high-change environments.
Read: Customized DDoS Testing Solutions for Enterprise Needs
Compare Layer 4 floods with Layer 7 application tests, metrics to capture, and mitigation patterns to verify after each simulation cycle.
Read: Complete Guide to Layer 4 & Layer 7 DDoS Attack SimulationsShutDown is intended exclusively for authorized resilience testing. You must verify ownership or obtain written permission before targeting any IP, hostname, or application. Government, banking, and educational properties require explicit approval—see our terms for blacklist and letter-of-authorization requirements.
Document every run with timestamps, concurrency settings, and observed metrics so your team can compare results over time, justify capacity investments, and show auditors that controls were exercised against realistic traffic—not just theoretical checklists.
Need help choosing concurrency, bypass profiles, or a paid tier? Our support team assists with authorized testing workflows, billing via cryptocurrency, and API access for automation—without sharing logs with third parties.